Dazr Identity developer docs
Standard OpenID Connect 1.0 with the authorization code flow and PKCE. No SDK needed: any certified OpenID Connect library works, and so does plain code.
People can already use their Google or Microsoft account inside Dazr Identity, so your app does not need separate Google and Microsoft buttons next to it: one button instead of three.
Discovery and endpoints
Everything is described in the discovery document. Point your library at the issuer and it finds the rest.
| What | Address |
|---|---|
| Issuer | https://identity.dazr.eu |
| Discovery | https://identity.dazr.eu/.well-known/openid-configuration |
| Authorization | https://identity.dazr.eu/oauth/authorize |
| Token | https://identity.dazr.eu/oauth/token |
| User info | https://identity.dazr.eu/oauth/userinfo |
| Public keys (JWKS) | https://identity.dazr.eu/oauth/jwks |
| Revocation (RFC 7009) | https://identity.dazr.eu/oauth/revoke |
| Introspection (RFC 7662), web server apps only | https://identity.dazr.eu/oauth/introspect |
| Sign-out (RP-initiated logout) | https://identity.dazr.eu/oauth/logout |
| Verification reports, web server apps only | https://identity.dazr.eu/oauth/verification-report |
Register an app
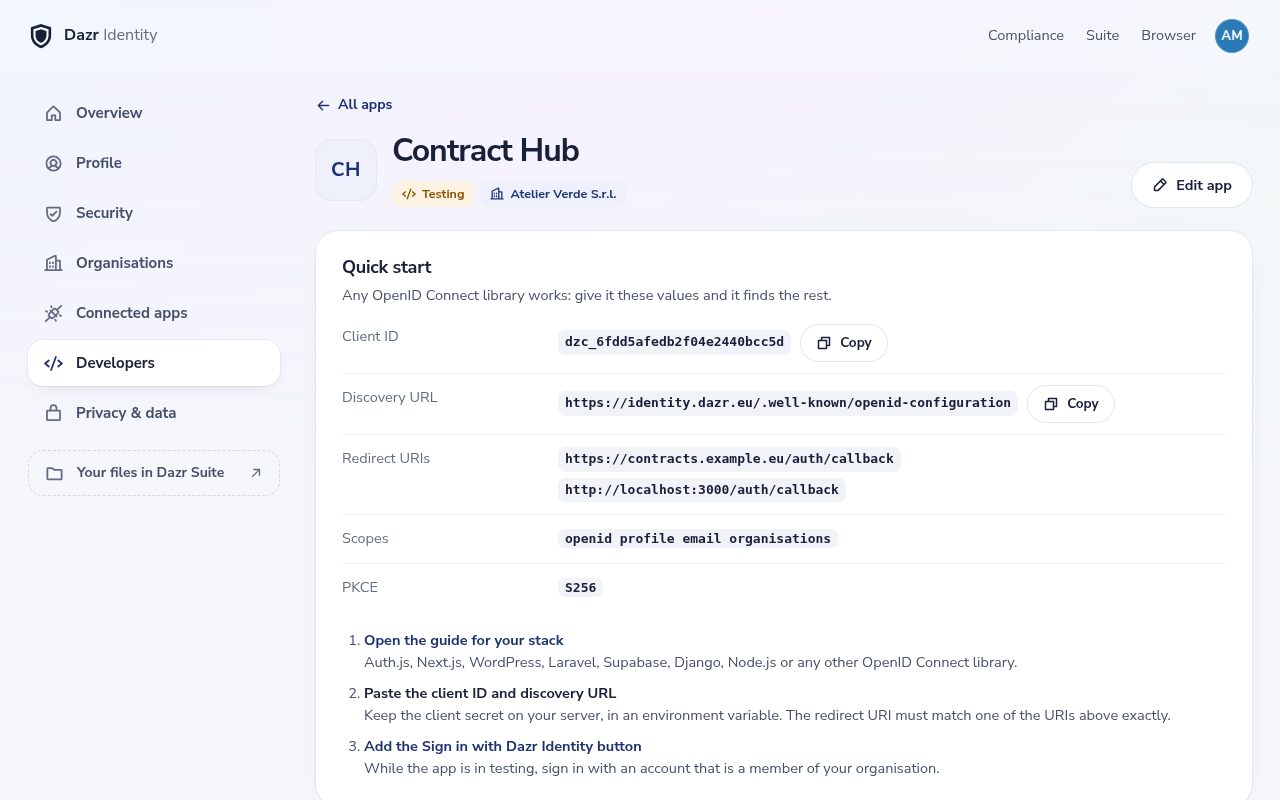
- Apps belong to an organisation. Owners and admins of the organisation register them in Developers.
- Web server apps (confidential clients) get a client secret, shown once. Authenticate to the token endpoint with HTTP Basic (
client_secret_basic) or in the form body (client_secret_post). - Single-page and mobile apps (public clients) get no secret. They send
client_idand rely on PKCE. - Redirect URIs match exactly. They must be
https://. While the app is in testing,http://localhostandhttp://127.0.0.1on any port also work. - A privacy policy address, a support email and a one-line purpose are required: people see them on the consent screen.
Integration guides
Every stack below uses its own standard OpenID Connect support. You need three values from the console: the client ID, the client secret (web server apps only) and the redirect URI you registered. The rest comes from the discovery document.
- Auth.js / NextAuth
- Next.js App Router
- WordPress
- Laravel
- Supabase
- Django
- Node.js (openid-client)
- ASP.NET Core
- Spring Boot
- Keycloak
- Any OpenID Connect library
sub claim is pairwise: the same for every app of your organisation, different for every other organisation. It never changes for a person, while an email address can. Store sub as the account key and treat email as contact data.
Any OpenID Connect library
If your stack is not listed, any OpenID Connect client works. Check these settings:
- Issuer
https://identity.dazr.eu, discovery URLhttps://identity.dazr.eu/.well-known/openid-configuration. - Response type
code(authorization code flow). No implicit or hybrid flow. - PKCE is required, with
code_challenge_method=S256. - Scopes:
openidplus only what you need fromprofile,email,address,organisationsandoffline_access. Your app must be registered for each scope it asks for. - Redirect URI: exactly as registered in the console, including the path and any query string.
- Client authentication:
client_secret_basicorclient_secret_postfor web server apps,nonefor single-page and mobile apps. - ID token signature: ES256. Some libraries assume RS256: set the algorithm to ES256.
- Use
subas the account key. It is pairwise, per organisation. - With
offline_access, store the new refresh token after every refresh: they rotate.
The flow
- Create a random
code_verifier(43 to 128 characters) and itscode_challenge= base64url(SHA-256(verifier)). Create a randomstateandnonce. Keep all three in the user's session. - Redirect to the authorization endpoint with
response_type=code,client_id,redirect_uri,scope(always includingopenid),state,nonce,code_challengeandcode_challenge_method=S256. - The person signs in if needed and sees the consent screen with the actual data. When they allow it, they come back to your redirect URI with
code,stateandiss. Check thatstatematches andissishttps://identity.dazr.eu. - On your server, POST to the token endpoint with
grant_type=authorization_code,code, the sameredirect_uriand thecode_verifier. - Verify the ID token: ES256 signature with a key from the JWKS (match the
kid),iss,aud= your client ID,expand yournonce. Usesubas the account key.
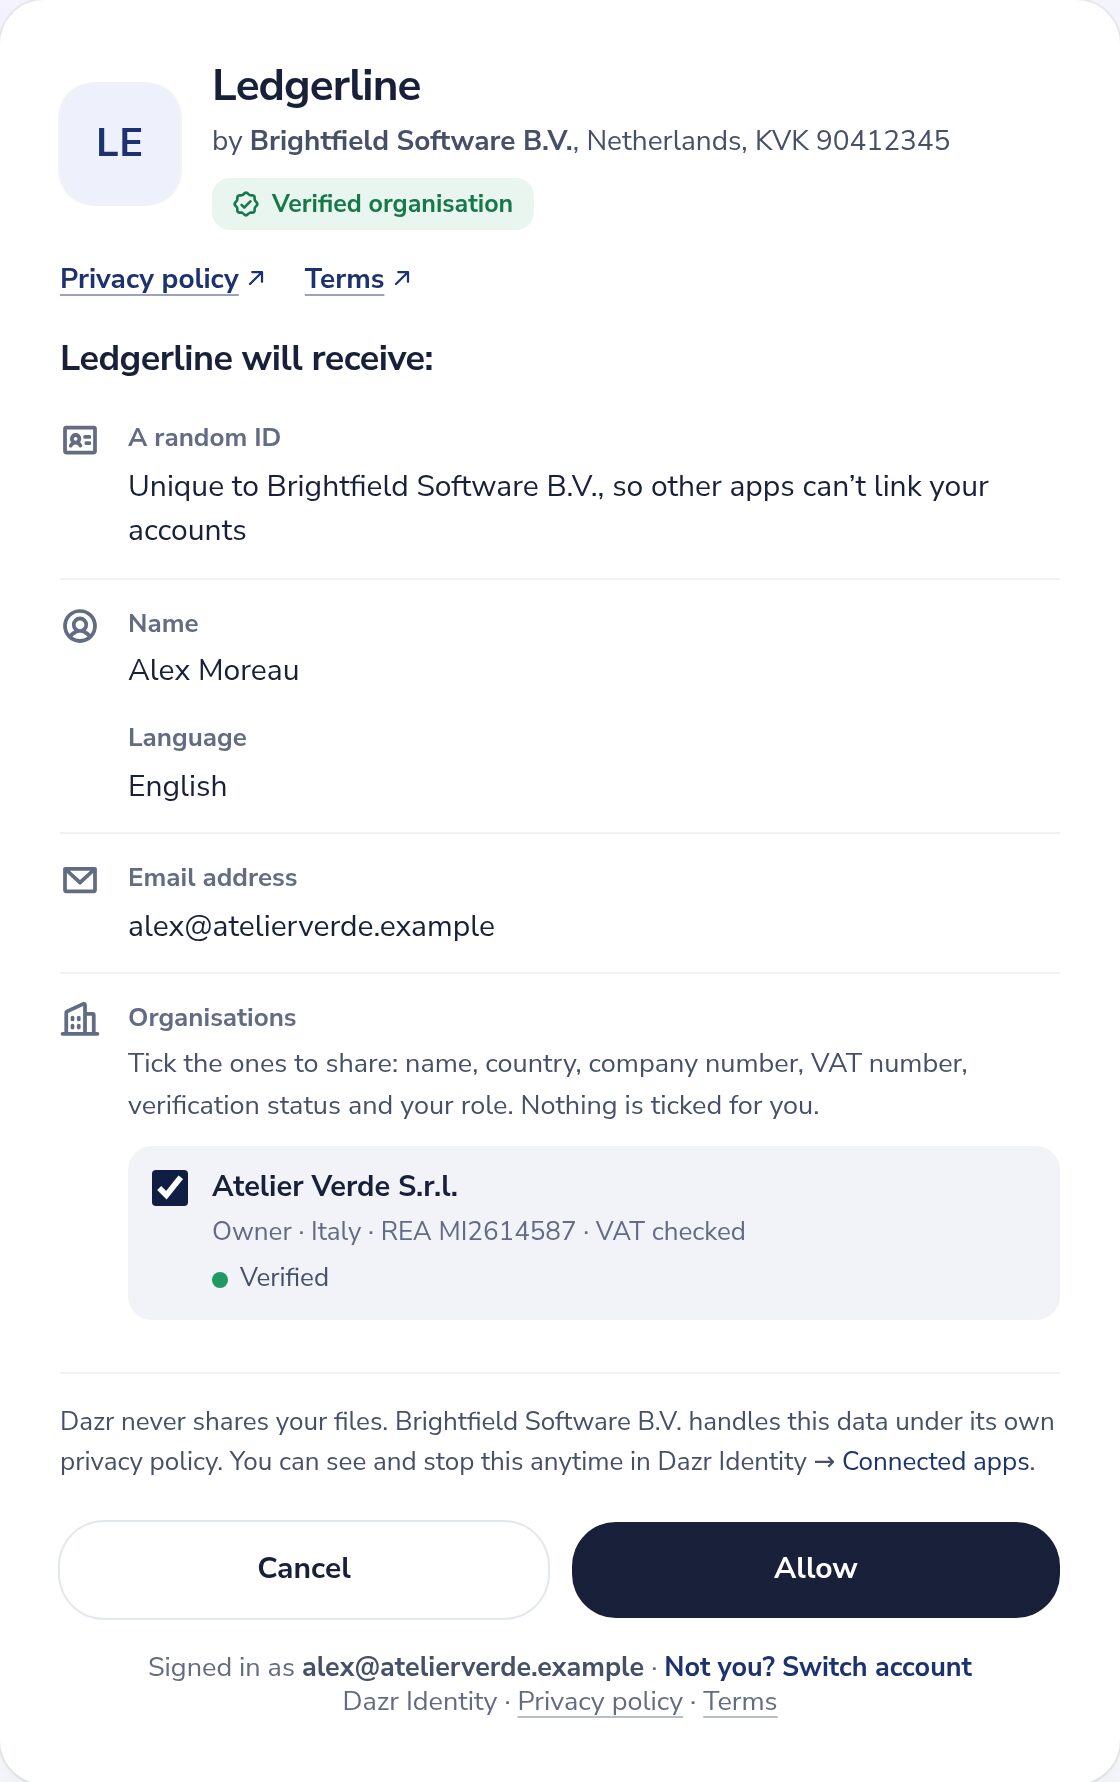
The prompt parameter accepts none (answer at once with login_required or consent_required if the person would have to act), login (ask the person to sign in again) and consent (show the consent screen even when it was approved before). max_age is supported. Remembered consent: if the person approved the same scopes before, they go straight back to your app. If you ask for more later, the consent screen lists only what is new.
Scopes and claims
Ask only for what you need. Nothing outside this table exists: no contacts, no passwords. Files are read only through the Dazr Files API, with its own files.read scope.
| Scope | Claims |
|---|---|
openid (required) | sub: a random ID for the person, the same for every app of your organisation and different for every other organisation |
profile | name (if set) and locale |
email | email and email_verified (always true) |
address | address (formatted, street_address, locality, region, postal_code, country), only if the person saved one |
organisations | organisations: the organisations the person ticks on the consent screen, each with id, name, display_name, website, country, register_number, vat, vat_verified (true only when the EU VIES service confirmed the VAT number), verified, verification (see Verified organisations) and role (owner, admin or member) |
offline_access | no claims; you also receive a refresh token |
Claims appear in the ID token for the scopes the person approved. The user info endpoint returns the same set, with current values.
Verified organisations
Dazr verifies an organisation only when official sources prove two things: who the person is, and that they represent this organisation, with its name, register number and VAT number. Typically its director signs a short declaration with a qualified electronic signature (QES) and adds the company register extract that lists them; with an extract sealed by the register, such as an Italian visura camerale or a Dutch KVK extract, it is instant, otherwise Dazr reviews it. A qualified signature alone never makes an organisation verified. Every organisation in the organisations claim carries its current verification:
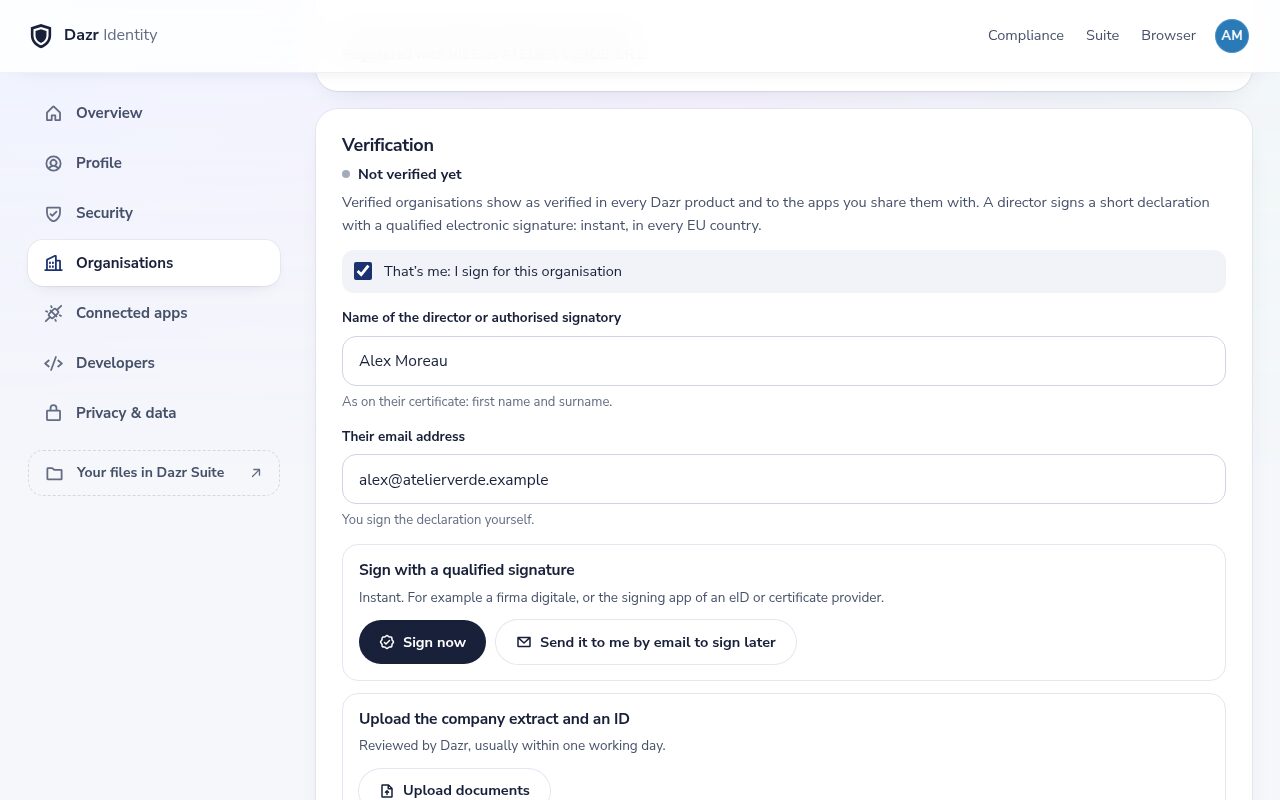
| verification.status | Meaning |
|---|---|
unverified | Not verified, or a verification failed, expired or was revoked (for example after the legal name or company number changed). |
pending | Verification is in progress: the representative has been asked to sign, the company register extract is still missing, or Dazr is reviewing documents. method says which way was started, for example qes (the representative signs the declaration), qseal, pec, letter, video or documents. |
verified | Verified. method is qes_org (qualified signature, the certificate names the organisation), extract_sealed (qualified signature or reviewed ID, plus an extract sealed by the business register), qes_reviewed (qualified signature, extract checked by Dazr), qseal (the organisation’s qualified electronic seal), documents, pec (a code sent to the organisation’s certified email address, PEC, Italy), letter (a code posted to the registered office), video (a video call with Dazr) or extract. authority says what proved that the person represents the organisation (see below), and verified_at is a Unix time. |
Only when the status is verified, verification.authority (and authority in webhooks) says how the link between the person and the organisation was proven. Every verification is documented evidence, checked once at the date shown. It is not a guarantee of the organisation’s solvency or conduct, and it does not show who owns the organisation.
| verification.authority | What it proves |
|---|---|
certificate | Documented evidence that the request was signed with a qualified electronic signature, or sealed with a qualified electronic seal, whose certificate names the organisation and its register number. Dazr checked the certificate against the EU trusted lists and for revocation. |
register_extract | Documented evidence that a director or legal representative confirmed the request, with a qualified electronic signature or an identity document checked by Dazr, and that an extract sealed by the business register, at most 3 months old, lists them. |
reviewed | Documented evidence that a director or legal representative confirmed the request, with a qualified electronic signature or an identity document, and that a person at Dazr checked a register extract, at most 3 months old, that lists them. |
pec | Documented evidence that someone with access to the organisation’s certified email address (PEC, Italy), as listed in the business register, confirmed the request with a one-time code. |
letter | Documented evidence that someone with access to the post at the registered office confirmed the request with a one-time code that Dazr sent there by letter. |
video | Documented evidence that a person at Dazr saw, in a video call, the identity document of the person who confirmed the request and an official extract that lists them as director or legal representative. |
The same definitions are in the terms of use, section 7 of the Developer Terms and every verification report.
The boolean verified stays for compatibility and equals verification.status === 'verified'. Each organisation also has an id, the same one webhooks use.
When the status is pending or verified, verification.report_url is the address of its verification report.
"organisations": [{
  "id": "org_3k9x2m0q8w1v5t7a", "name": "Conti Logistica S.r.l.", "country": "IT",
  "register_number": "REA MI1234567", "vat": "IT12345678903", "vat_verified": true,
  "display_name": "Conti", "website": "https://conti.example",
  "verified": false, "verification": { "status": "pending", "method": "qes" }, "role": "owner"
}]
role and membership are read again at every token refresh and user info request: after a role change the next response carries the new role, and an organisation the person left or was removed from is no longer included. When an admin of the organisation disconnects your app, the organisation is left out of tokens issued before, until a member shares it with your app again in a new sign-in. display_name and website are null when the organisation has not set them; name is always the legal name.
Countries and times
Organisations in the 27 EU countries, Norway, Iceland, Liechtenstein, Switzerland and the United Kingdom can verify. The fastest route depends on the country:
| Country | Organisation verification | Business verification |
|---|---|---|
| Italy | Instant with a qualified signature and a visura sealed by the business register, or a few minutes with a code to the company’s certified email address (PEC) | A visura no older than 3 months, checked by a person at Dazr, usually within one working day |
| Netherlands | Instant with a qualified signature and a digitally certified KVK extract | From the KVK register, checked by a person at Dazr, usually within one working day |
| Austria, Belgium | Instant with a qualified signature and an extract sealed by the business register | An official extract no older than 3 months, checked by a person at Dazr, usually within one working day |
| Norway, Denmark, Finland, France, Poland, Czechia | Instant with a qualified signature whose certificate names the organisation; otherwise an extract and an ID, checked by a person at Dazr, usually within one working day | From the online business register, checked by a person at Dazr, usually within one working day |
| United Kingdom | An extract and an ID, checked by a person at Dazr, usually within one working day | From Companies House, checked by a person at Dazr, usually within one working day |
| Every other supported country | Instant with a qualified signature whose certificate names the organisation; otherwise an extract and an ID, checked by a person at Dazr, usually within one working day | An official extract no older than 3 months, checked by a person at Dazr, usually within one working day |
| Everywhere | A code by post (€100 excl. VAT, 3 to 10 working days) or a video call (€200 excl. VAT) | A video call (€200 excl. VAT) when the representative has no phone camera |
Times are typical, not guaranteed. Automatic means that documented rules decide when every check is clear; when one is not, a person at Dazr looks, usually within one working day. The help page for people asked to verify lists which register extract to get in each country.
Require a verified organisation
In the console, set Require a verified organisation to Verification started or Verified, or ask per request with acr_values=urn:dazr:org:verification-started or acr_values=urn:dazr:org:verified (the stricter of the two wins). Your app must also request the organisations scope.
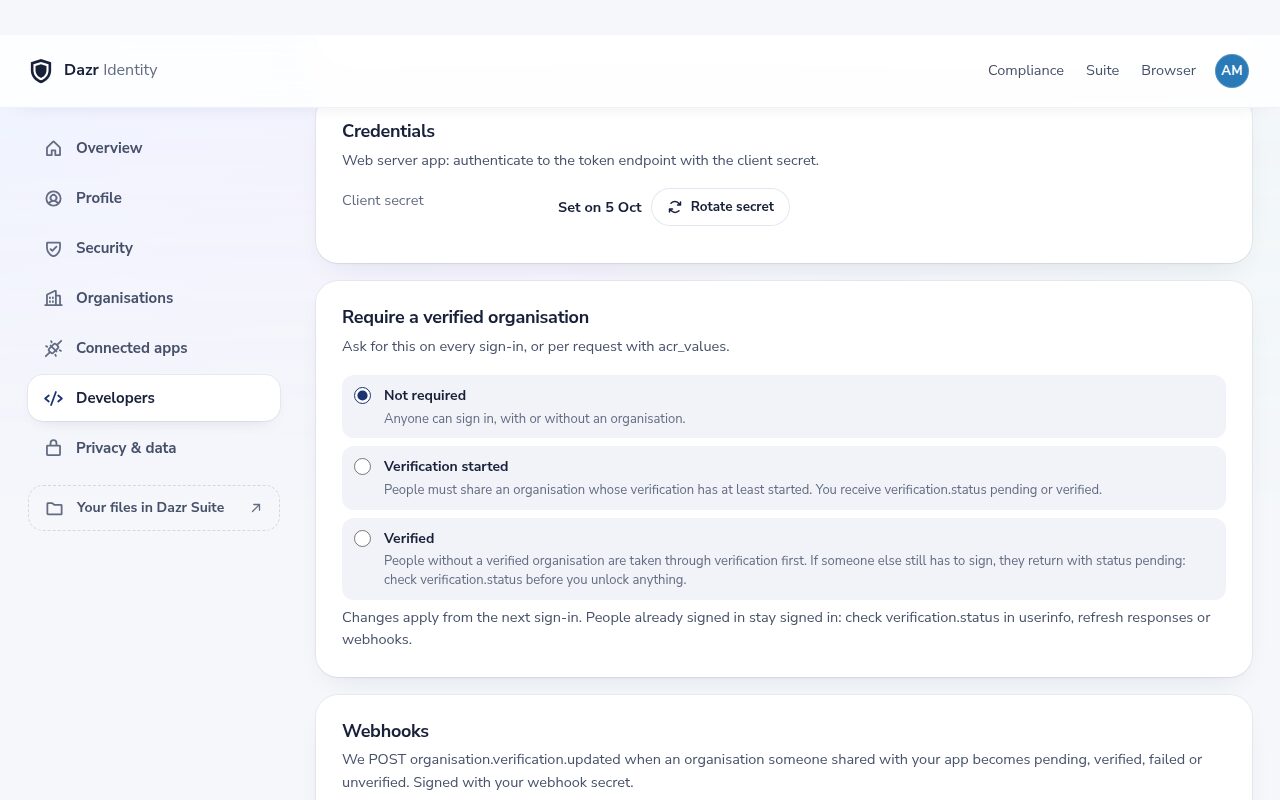
Someone without a qualifying organisation is taken through it in the same sign-in: their name, the organisation (with the VAT number checked in VIES), then the verification. They can sign right away, have the declaration emailed to themselves, or name someone else who signs. They then tick the organisation on the consent screen (only qualifying organisations can be ticked) and return to your redirect URI.
If someone else still has to sign, the person comes back with status pending, also when you asked for Verified: you receive a code, the claim says pending, and the ID token's acr is urn:dazr:org:verification-started instead of urn:dazr:org:verified. Always gate on verification.status, never on the fact that sign-in succeeded. With prompt=none you get interaction_required when the requirement isn't met.
Changes to the setting apply from the next sign-in. People already signed in are not signed out: refresh responses, the user info endpoint and webhooks always carry the current status, so use those to react for existing sessions.
Webhooks
Add a webhook URL (https) in the console. You see the signing secret once; you can rotate it. Dazr sends organisation.verification.updated when an organisation that one of your users shared with your app becomes pending, verified, failed or unverified. Apps that never received an organisation through consent never hear about it.
POST /your/webhook
Content-Type: application/json
Dazr-Event: organisation.verification.updated
Dazr-Delivery: dlv_8Fq2…
Dazr-Signature: t=1791021600,v1=5e0c…

{ "id": "evt_…", "type": "organisation.verification.updated", "created": 1791021600,
  "data": { "organisation": { "id": "org_3k9x2m0q8w1v5t7a", "name": "Conti Logistica S.r.l.", "country": "IT" },
            "status": "verified", "method": "qes_org", "authority": "certificate", "verified_at": 1791021598,
            "report_url": "https://identity.dazr.eu/oauth/verification-report?org=org_3k9x2m0q8w1v5t7a",
            "subjects": ["Xo1c…"] } }
status is pending, verified, failed or unverified. subjects are the sub values, at your app, of the people who shared this organisation with it. Check the signature before you trust the body:
import crypto from 'node:crypto';
// raw = the request body exactly as received (a string), header = the Dazr-Signature header
function verifyDazrSignature(raw, header, secret) {
  const m = /^t=(\d+),v1=([a-f0-9]{64})$/.exec(header || '');
  if (!m || Math.abs(Date.now() / 1000 - Number(m[1])) > 300) return false; // reject old deliveries
  const want = crypto.createHmac('sha256', secret).update(m[1] + '.' + raw).digest('hex');
  return crypto.timingSafeEqual(Buffer.from(want), Buffer.from(m[2]));
}
Answer with any 2xx within 8 seconds. Otherwise Dazr retries after about 5 minutes, 30 minutes, 2, 6, 12 and 24 hours, then marks the delivery failed. Every attempt has the same Dazr-Delivery ID, so ignore duplicates. The console lists recent deliveries, can resend one and can send a test event (webhook.test). Polling the user info endpoint works too.
Organisations and roles in your app
In a portal for business customers, map each Dazr organisation to a customer account (a tenant) in your app, and the person’s role in that organisation to a role in your app.
- Request the
organisationsscope. Each organisation the person ticks arrives with itsid,role(owner,adminormember) andverification. - Key the tenant on
organisations[].id, never on the name or the VAT number: those can change. - Map the role, for example
ownerandadminto your administrator role andmemberto your user role. Read it again at every sign-in and token refresh: roles change and people leave. - Unlock business features only when
verification.statusisverified, orkyb.statusisapprovedwhere you need business verification.
// claims: the ID token claims or the user info response
const ROLE = { owner: 'tenant_admin', admin: 'tenant_admin', member: 'tenant_user' };

const memberships = (claims.organisations || []).map((o) => ({
  tenantId: o.id,                              // e.g. org_3k9x2m0q8w1v5t7a
  role: ROLE[o.role] || 'tenant_user',
  verified: o.verification?.status === 'verified',
  businessVerified: o.kyb?.status === 'approved',
}));
With Keycloak
When Keycloak brokers Dazr Identity (see the Keycloak guide), add mappers under the identity provider’s Mappers tab, with sync mode Force. Keycloak reads these paths from the user info response, and a path can name one position in a list: organisations[0] is the first organisation the person ticked. For a portal with one customer account per person that is enough; if people work for several organisations, let them tick one, or read the full list in your app.
| Mapper type | Claim | Result |
|---|---|---|
| Attribute Importer | organisations[0].id | User attribute dazr_org_id: the tenant key |
| Attribute Importer | organisations[0].name | User attribute dazr_org_name |
| Claim to Role | organisations[0].role, claim value owner | Realm or client role tenant_admin |
| Claim to Role | organisations[0].role, claim value admin | Realm or client role tenant_admin |
| Claim to Role | organisations[0].role, claim value member | Realm or client role tenant_user |
| Claim to Role | organisations[0].verification.status, claim value verified | Role verified_business |
Then add a User Attribute mapper for dazr_org_id to your app’s client scope in Keycloak, so your app receives the tenant key in Keycloak’s own tokens, next to the roles.
Business verification (KYB)
Business verification, often called KYB (know your business), is the higher assurance level on top of organisation verification. It adds the business register, an ID check with a live selfie for the person acting for the company (the representative), and screening of the company and the representative against sanctions lists and lists of politically exposed persons (PEP). Beneficial owners are not part of it.
It costs €25 excl. VAT per organisation, once. The organisation pays, or your app pays for its customers from prepaid credit. If it stops before any ID has been checked, the payment is refunded in full.
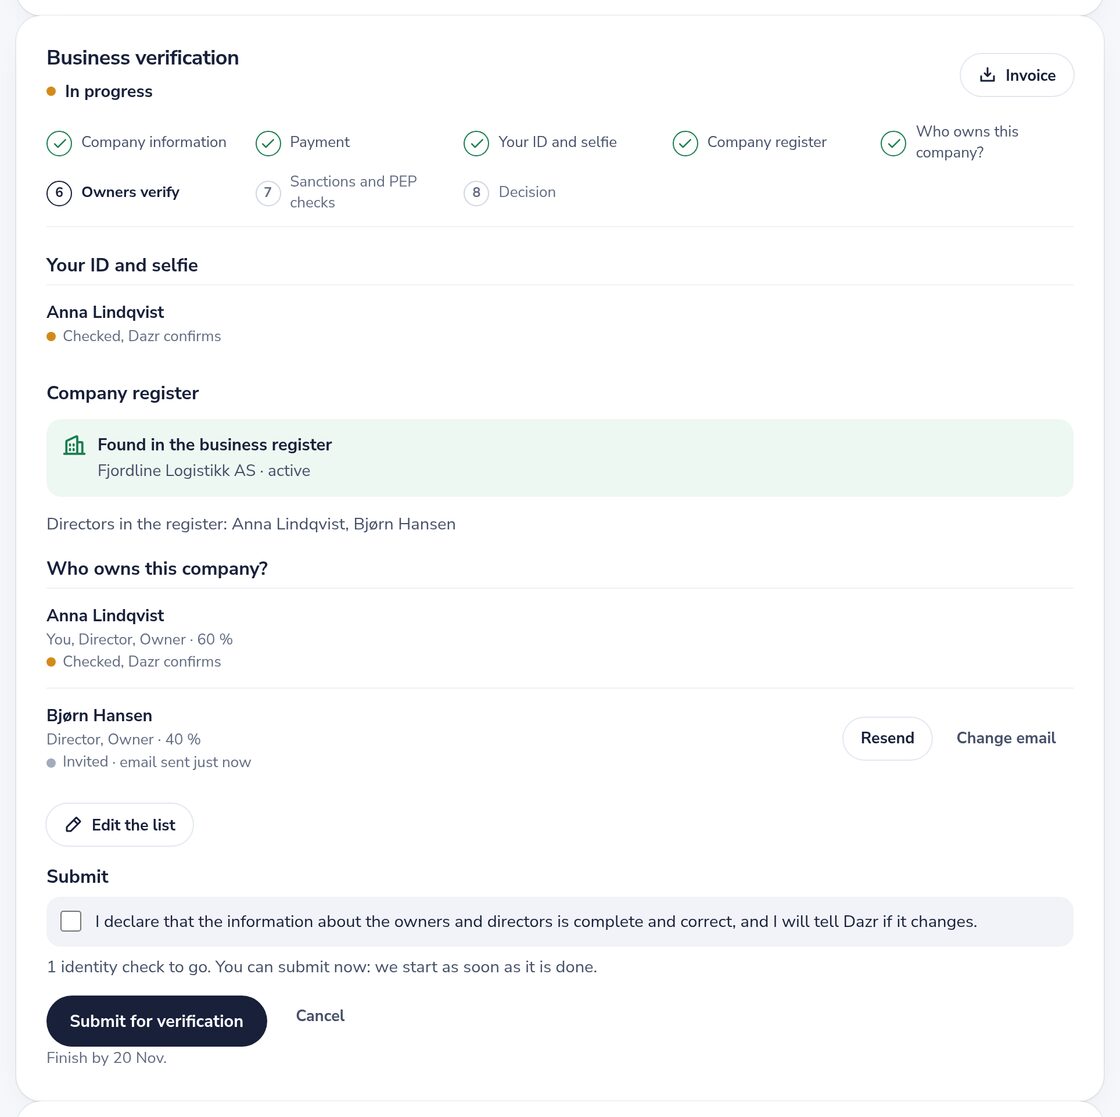
- Company information. The legal form, and the register number and registered office from the organisation’s legal details, confirmed by the person who starts it.
- Payment. €25 excl. VAT through Mollie, with an invoice on the organisation page. When your app pays from its prepaid credit, the organisation skips this step.
- ID and selfie. The person who starts it is a director or legal representative, or names one, who gets an email link with a one-time code (valid 14 days, reminders after 2 and 7 days), confirms their role and may add a power of attorney. The representative takes one photo of a passport (the photo page), ID card or residence permit (the front) and one front-facing selfie, live with the camera on the page; nothing can be uploaded. An AI model reads the document; Dazr checks the dates and the name, and for a passport the machine-readable zone (ICAO 9303 check digits). A Dazr reviewer compares the selfie with the document photo. On a computer the step shows a QR code that moves the capture to a phone, and the computer continues on its own. Without a phone camera, the representative can book a video call with Dazr instead (€200 excl. VAT, refunded in full if Dazr cancels or offers no time).
- Company register check. Name, status and directors from the official register where one is online (Norway, Denmark, Finland, France, the Netherlands, Poland, Czechia and the United Kingdom), otherwise from an official extract no older than 3 months, which Dazr reads automatically.
- Sanctions and PEP checks. The company and the representative against the EU, UN and OFAC sanctions lists and for politically exposed persons. Where the PEP database is not available, a name-only lookup in Wikidata gives an indication. The PEP result is recorded in the claim and the report and never stops the approval.
- Decision. A Dazr reviewer compares the selfie with the document photo and decides, with the results of the documented risk rules: they show when the ID check fails, a name matches a sanctions list, the register does not list the representative, or the company is not confirmed. The reviewer can approve, reject with a reason, ask the organisation for more information or run a check again, usually within one working day. High-risk cases need two reviewers. No case is rejected automatically.
Approved organisations are screened against the sanctions lists again every day and for PEP status every 30 days. A new sanctions hit moves the verification back to review; a new PEP hit is flagged and the verification stays approved. Either way your app hears about it.
An approved business verification is documented evidence that a director or legal representative, whose identity document and live selfie were checked, confirmed the request, that the business register or an official extract at most 3 months old shows the company, and that the company and that person were screened against sanctions lists and lists of politically exposed persons. Beneficial owners are not checked.
The kyb claim
Every organisation in the organisations claim carries kyb, and verification.assurance_level sums up both levels: none, basic (organisation verified) or kyb (business verification approved).
| kyb.status | Meaning |
|---|---|
none | No business verification, or the last one was cancelled or expired. |
in_progress | Started: the organisation is completing the steps. |
in_review | Submitted and being reviewed by Dazr, or back in review after a new screening hit. |
approved | Approved. Only then does the claim include verified_claims. |
rejected | Not approved. The organisation can start a new one. |
When approved, verified_claims follows the OpenID Connect for Identity Assurance format:
"kyb": {
  "status": "approved",
  "report_url": "https://identity.dazr.eu/oauth/verification-report?org=org_3k9x2m0q8w1v5t7a",
  "verified_claims": {
    "verification": {
      "trust_framework": "dazr_kyb", "assurance_level": "kyb", "time": "2026-10-06T09:14:03.000Z",
      "verification_process": "kyb_7Tq2…",
      "evidence": [
        { "type": "electronic_record", "check_details": [{ "check_method": "data", "organization": "no-brreg" }] },
        { "type": "document", "check_details": [{ "check_method": "vpip" }, { "check_method": "pvr" }],
          "note": "ID document and a live, front-facing selfie of the representative; beneficial owners are not part of this verification" }
      ]
    },
    "claims": {
      "legal_name": "Fjordline Logistikk AS", "country": "NO", "registration_number": "912345678",
      "beneficial_owners": "not_verified",
      "started_by_representative": false,
      "screening": { "result": "no_match_found", "pep_checked": true, "last_screened_at": "2026-10-06T03:23:00.000Z" },
      "risk_level": "low"
    }
  }
}
beneficial_owners is always not_verified: business verification covers the company and the person acting for it, not who owns it. started_by_representative says whether the person who started it is also the representative whose ID was checked, or invited them by email. The claim never contains names, dates of birth or document details. Those stay in the audit report, which your app can fetch for organisations shared with it.
Require business verification
In the console, set Require a verified organisation to Business verification (KYB), or ask per request with acr_values=urn:dazr:org:kyb. Someone without it goes through every step in the same sign-in, one screen at a time, and continues to your app once Dazr has approved it; until then they get an email when it is approved and sign in again. The ID token’s acr is urn:dazr:org:kyb only once an organisation is approved, so always gate on kyb.status === 'approved' before you unlock anything that needs it.
Webhooks for business verification
The same organisation.verification.updated event is sent when the business verification status changes, including after re-screening. Its data adds:
"kyb": { "status": "approved", "approved_at": 1791021598, "risk_level": "low" },
"assurance_level": "kyb"
Business verification on its own
An organisation can also start business verification on its own, at https://identity.dazr.eu/verify/business?org=…, linked from its page in Dazr Identity, without any app asking for it. The result is the same: one verification per organisation, which every app it shares the organisation with can rely on. Images of ID documents and selfies are deleted 30 days after the decision; the results and the report are kept for 5 years after the verification ends, as anti-money laundering rules require.
How the decision is made
A Dazr reviewer decides every business verification, usually within one working day, and compares the selfie with the document photo. The reviewer takes a closer look when one of these applies:
- The identity check failed or was unsure. The face does not match the document photo, the selfie is not one clear, frontal face, the document cannot be read with enough confidence, shows signs of tampering or of a screen, is expired, or belongs to someone under 18, or the name on the ID differs from the representative’s.
- A sanctions match. A name matches the EU, UN or OFAC sanctions lists at or above the match threshold, or sanctions screening could not run.
- No authority. The register or the official extract lists directors, and the person on the ID is none of them.
- The company is not confirmed. The register has no company with this number, it is not active, its legal name differs, or there is no matching extract.
Everything else is recorded and never blocks the approval. A possible politically exposed person (PEP) is flagged as screening.pep possible_match in the claim and the report; if the PEP database is not available, the claim says indication_only or not_screened. When the register lists no directors, authority is declared_by_representative. Decide yourself whether you need enhanced due diligence.
Countries without an online register
In countries without a live register, such as Italy, Germany, Spain or Belgium, the organisation uploads an official extract (a visura camerale, a Handelsregisterauszug, a nota simple). Dazr reads it automatically and checks the company name, the register number, the date (at most 3 months old) and the directors listed. A match is approved like a live register; a mismatch or an extract that cannot be read goes to a reviewer. A sealed extract is also checked for its register seal.
PEP, authority and flags in the claim
Field in verified_claims.claims | Meaning |
|---|---|
screening.pep | no_match_found, possible_match (flagged, not blocking), indication_only (only a name lookup in Wikidata ran) or not_screened. |
authority | What showed that the representative may act: register, extract, dazr_verification or declared_by_representative. |
flags | Present when there is something to look at: pep_possible_match, high_risk_country. |
Verification reports for audits
For every organisation shared with your app you can fetch a report of how and when Dazr verified it, for your audit file. It exists while the organisation is verified, and while its verification is in progress, showing what is done so far.
- The organisation: name, country, register number, VAT number and registered office.
- The verification: status, method, authority, and when it was requested, signed and verified.
- The evidence: for a qualified signature or seal, the signer's name as on the certificate, the certificate's issuer, serial number, validity and SHA-256 fingerprint, its qualified status (QC statements, trust service provider and service from the EU trusted list, with the list's sequence number and issue date), the signing time and the revocation check. For a register-sealed extract, who sealed it, when, and what matched: name, register number, VAT number, director. The VIES result. For a PEC code, a letter or a video call, the dates and the checks a Dazr reviewer ticked, shown as "Dazr reviewer" with an internal ID.
- For your files: the SHA-256 fingerprint of every evidence file, a document ID, when the report was generated, and a short explanation of each method and of what authority means.
A report never contains ID document images or numbers, one-time codes, the PEC address, email addresses, or any address other than the registered office.
Sample reports
Two sample reports with a made-up organisation and made-up people, so your compliance team can see what you receive. They are signed with a sample key, not with Dazr’s keys: verify them with the sample public key below, never against the production JWKS.
- Organisation verification (qualified signature): PDF, signed JSON (JWS)
- Business verification: PDF, signed JSON (JWS)
- The sample public key (JWKS)
Fetch a report
Authenticate with your client ID and client secret, as at the token endpoint: HTTP Basic (client_secret_basic), or the form body of a POST (client_secret_post). Never put the secret in the URL. Use the organisation id from the claims or webhooks, or simply the verification.report_url they carry.
curl -u "$DAZR_CLIENT_ID:$DAZR_CLIENT_SECRET" -o report.pdf \
"https://identity.dazr.eu/oauth/verification-report?org=org_3k9x2m0q8w1v5t7a&format=pdf&lang=en"| Parameter | Meaning |
|---|---|
org | The organisation id. |
format | pdf (default) or jws, the same facts as signed JSON. |
lang | Language of the PDF: en (default), nl, it, de, fr, es or pl. |
doc | Instead of the report: declaration, the director's signed declaration (qualified signature or seal only), or extract, the company register extract. |
Only organisations that at least one of your users shared with your app through consent can be fetched. Any other organisation answers 404, the same as one that doesn't exist or has no verification; a wrong client secret answers 401. Apps without a client secret cannot fetch reports. Downloads are rate limited, and each one shows in the organisation's activity for its admins, with your app's name. In the console, your app's page lists the connected organisations with the same downloads.
Verify the signed JSON
With format=jws you receive a compact JWS (ES256, header typ dazr-verification-report+jwt), signed with the same keys as ID tokens. Its claims are iss, iat, jti (the document ID), sub (the organisation id), aud (your client ID) and report, the facts. The PDF carries the same JWS on its last page and in its metadata (DazrVerificationReport), so a PDF can be checked offline too.
import { createRemoteJWKSet, jwtVerify } from 'jose';

const jwks = createRemoteJWKSet(new URL('https://identity.dazr.eu/oauth/jwks'));
// jws = the response body of format=jws, or the text from the PDF metadata
const { payload } = await jwtVerify(jws, jwks, {
  issuer: 'https://identity.dazr.eu',
  audience: process.env.DAZR_CLIENT_ID,
  typ: 'dazr-verification-report+jwt',
});
console.log(payload.report.verification.status, payload.report.verification.authority);
Let an auditor check the signature
For a qualified signature or seal, doc=declaration returns the signed declaration exactly as it was uploaded: a signed PDF (PAdES) or a .p7m file (CAdES). An auditor can validate it independently with the European Commission's DSS demo validator: upload the file, keep the default validation policy and run it. The result shows whether the signature is qualified (QESig, or QESeal for a seal), who signed, and the trust service provider from the EU trusted list. doc=extract returns the company register extract; a register-sealed extract can be validated the same way.
The report is evidence for your audit file. Regulated firms remain responsible for their own customer due diligence.
Dazr keeps the signed declaration, the extract and the report data while the organisation is verified and for 5 years after its verification ends or the organisation is deleted. Keep your own copies for as long as your rules require.
Keys for old reports
Reports are signed with the same keys as ID tokens, and those keys rotate. Every key that ever signed a report stays published at https://identity.dazr.eu/oauth/jwks/archive, with dazr_status current, previous or retired, for at least 5 years after its last use. Verify an old report against the archive when its kid is no longer in the JWKS.
Identity verification (KYC)
Switch on Allow identity verification when a sign-in asks for it in the console, then ask for a verified person with acr_values=urn:dazr:person:kyc. Or tick Require identity verification on every sign-in. Without either setting, the acr value is ignored and nothing is charged. No extra scope is needed. During the sign-in, the person takes a live photo of their ID and one selfie on their phone; a computer shows a QR code. Dazr reads the document, compares the faces and screens the name against the EU, UN and OFAC sanctions lists. A person at Dazr reviews every check, usually within one working day.
Each verification costs €1.50 excl. VAT, from your organisation’s balance. The person never pays. A verification stays valid for 12 months. When another app asks for it, the person agrees on a consent screen instead of taking new photos, and that app pays €1.50, once per verification. Your app asking again with prompt=consent, or a sign-in with a verification your app already received, is free.
The ID token and user info carry the kyc claim, and acr is urn:dazr:person:kyc:
"kyc": {
  "verified": true, "verified_at": 1791356184, "valid_until": 1822892184,
  "given_name": "ANNA", "family_name": "LINDQVIST", "birthdate": "1985-03-15",
  "nationality": "NO", "document_country": "NO",
  "sanctions": { "status": "no_match", "screened_at": 1791356184, "lists": ["eu", "un", "ofac"] }
}
sanctions.status is no_match, or cleared_by_review when a listed name was similar and a reviewer found it is not this person. Document images and numbers are never shared. After 12 months the claim says "verified": false: ask again.
interaction_required: withprompt=none, when the person still has to verify or agree.temporarily_unavailable: your balance cannot pay. The person is told your app can’t verify them right now, and your admins get an email.access_denied: the person cancelled, or a reviewer still has to decide.
Verifications are real and charged while your app is in testing too.
Balance
Your organisation can pay for your customers’ business verification. In the console, open your app and tick We pay for our customers’ business verification. The price is taken from your organisation’s balance, one balance for every app of the organisation and for paid Dazr APIs. A verification costs €25 excl. VAT. When the balance is too low, your customer pays as usual, and your admins get an email.
Your app pays only for a sign-in that asks for business verification, and once per customer organisation. What an app pays per day for identity and business verification has a limit: €250 excl. VAT, unless you change it under Daily limit for verifications in the console. When it is reached, until the next day new identity verifications are refused, your customers pay for their own business verification, and your admins get an email.
- Identity verification. €1.50 per verification, and each time a verification is shared with another app. Bonus credit can pay for it.
- Deposits. From €100, through Mollie, for businesses only: your organisation must be verified or have a VAT number confirmed by VIES. You get an invoice with VAT.
- Bonus credit. +10 % from €1,000, +20 % from €5,000 and +40 % from €10,000. The balance shows paid credit and bonus credit; paid credit is used first.
- Non-refundable. Deposits to the balance are non-refundable and are never paid out: they can only be used for paid Dazr API usage, such as business verification. Bonus credit has no cash value.
- Returns. A verification cancelled before any ID check returns its price to the balance. A chargeback takes the deposit and its bonus back; a balance below zero pauses paid use until the next deposit.
- Ledger. Every deposit, bonus, use and return, with the running balance, in the console and as CSV.
Test mode
While your app is not live, a business verification started from a sign-in to it gives a test outcome. There is no payment, no ID photo and no reviewer, and the organisation’s real verification does not change. The last four digits of the organisation’s register number or VAT number choose the outcome:
| Last four digits | Outcome | kyb.status |
|---|---|---|
0001 or any other number | Approved | approved |
0002 | Not approved | rejected |
0003 | Sent to a reviewer | in_review |
0004 | Sanctions match | in_review |
0005 | Expired | none |
Test outcomes carry test: true in the claim, the webhook and the report, and only your app sees them while it is not live. Register numbers are unique on Dazr, so use your own, for example a Dutch KVK number like 1234 0002. In the console you can also send a test webhook for each outcome.
Tokens and lifetimes
| Token | Lifetime and rules |
|---|---|
| Authorization code | 60 seconds, single use, bound to your client, redirect URI and PKCE challenge. Using a code twice revokes the tokens it issued. |
| Access token | 10 minutes. A signed JWT (ES256, typ at+jwt) with aud = your client ID. Send it as Authorization: Bearer. |
| ID token | 10 minutes. ES256, with iss, sub, aud, exp, iat, auth_time, nonce and amr where known. |
| Refresh token | Only with offline_access. Rotates on every use: always store the new one. Sending an old refresh token again revokes the whole sign-in. Expires after 30 days without use and 180 days at most. |
Signing keys rotate. Always pick the key by kid from the JWKS and refresh the JWKS when you see an unknown kid.
How the person signed in
The ID token’s amr (RFC 8176) says how the person signed in: ["otp"] for a one-time code by email, ["hwk", "user"] for a passkey with user verification, and ["fed"] for Google or Microsoft.
Language
Send ui_locales with the authorization request, for example ui_locales=de-AT de en. The first language Dazr supports is used for the sign-in and consent screens. The supported languages are in ui_locales_supported in the discovery document.
The sign scope
The sign scope in the discovery document is for the Dazr Sign API only. It lets an app send documents for signature on behalf of the person, and you enable it in the Dazr Sign portal. Sign in with Dazr Identity does not need it.
Dazr Files API and WebDAV (read only)
The Dazr Files API lets your app list and download files from Dazr Files, for example to back them up. It is read only: no request can upload, change, move, share or delete anything. Turn it on for your app in the console, on your app’s page under Dazr Files API. It uses the same app, client ID and secret as Sign in with Dazr Identity, and the same access tokens.
There are two ways in. An organisation’s owner or admin approves your app for the organisation’s shared files, and your server then gets tokens without a person (best for unattended backups). Or a person allows your app with the files.read scope, and your app reads that person’s own files.
The full reference, with every endpoint, examples, errors, limits, the changes feed and WebDAV setup for rclone and Synology, is in the Dazr Files API docs.
Organisation settings that affect sign-in
- Members must use passkeys. Owners and admins can turn this on. Members then sign in with a passkey to every app that asks for the
organisationsscope; a sign-in with an email code, Google or Microsoft is sent back to sign in with a passkey, andprompt=noneanswerslogin_required. - Verified email domain. An organisation proves its email domain with a DNS record. If the organisation allows it, people who sign in with an address at that domain are offered to join, straight away or after an admin approves. A verified domain does not verify the organisation itself and is not in the claims.
Errors
As long as your client ID and redirect URI are valid, errors come back to your redirect URI as error, error_description, state and iss: for example invalid_request (such as missing or plain PKCE), invalid_scope, unsupported_response_type, access_denied (the person cancelled, or the app is in testing and the person is not a member), login_required, consent_required and interaction_required (with prompt=none, when a required verified organisation is missing). With an unknown client or an unregistered redirect URI, Dazr shows an error page and never redirects. The token endpoint answers with JSON errors such as invalid_client, invalid_grant and unsupported_grant_type.
Sign-out
To sign someone out, send them to the sign-out endpoint with id_token_hint (or client_id), an optional post_logout_redirect_uri registered in your app settings, and state. Dazr asks whether they also want to sign out of Dazr Identity on that device, then sends them back. Revoke refresh tokens you no longer need at the revocation endpoint.
Testing and going live
A new app is in testing: only members of your organisation can sign in, and the consent screen says so. To go live, get your organisation verified in Dazr Identity, add an https:// redirect URI and request a live review in the console. Changing the name, purpose, privacy policy or data of a live app needs a new review.
Transfer an app to another organisation
An app can move to another organisation registered on Dazr, for example after a sale or a reorganisation. An owner or admin starts the transfer under Transfer app in the app’s settings, in Dazr Identity or in the Sign portal. An owner or admin of the other organisation accepts or declines it within 14 days. Until then, the sender can cancel and nothing changes.
- Who can receive it. Only an organisation registered on Dazr, named by its organisation ID. Its owners and admins find the ID in its legal details in Dazr Identity. A live app, an app in review, an app that requires a verified organisation and an app with the Dazr Sign API enabled can only move to a verified organisation. This is checked again when the transfer is accepted.
- A recent sign-in. Starting and accepting a transfer need a sign-in from the last 10 minutes.
- What moves. The client ID, the settings, the logo, the redirect URIs, the enabled APIs and the webhook URLs. The admin who accepts also accepts the Developer Terms for the new organisation.
- The client secret. A web server app gets a new client secret, shown once to the admin who accepts. The previous secret keeps working at the token, revocation and introspection endpoints for the grace period chosen when the transfer started: none, 24 hours (the default) or 7 days. Verification reports need the new secret.
- Webhooks. The URLs stay. Their signing secrets, for Dazr Identity and for Dazr Sign, are renewed and shown once to the admin who accepts. Deliveries from before the transfer are not sent again.
- People and their
sub. Every person keeps the samesubin the app, so the accounts in your app keep working. It differs from theirsubin the new organisation’s other apps. People approve the app again at their next sign-in, because the consent screen now names the new organisation. Tokens issued before the transfer stop working. - What stays with the previous owner. Sign-in and consent counts and webhook deliveries from before the transfer. Documents created through the Dazr Sign API stay with the people who own them, and the app’s new owner cannot see them.
The button
Use the wording "Sign in with Dazr Identity" and the Dazr logo as below. You may change the size, not the logo, colours or wording. Link it to your own route that starts the flow.
<a href="/auth/dazr" style="display:inline-flex;align-items:center;gap:10px;height:44px;padding:0 18px;border-radius:22px;background:#18203a;color:#fff;font: 600 15px/1 'Dazr', system-ui, sans-serif;text-decoration:none">
  <svg width="20" height="20" viewBox="0 0 100 100" aria-hidden="true"><path d="M64.133 21.813 A6.634 6.634 0 0 1 66.455 31.054 A2.552 2.552 0 0 0 67.912 34.849 A36.74 36.74 0 0 1 93.010 60.100 A2.654 2.654 0 0 1 88.914 62.984 A44.91 44.91 0 0 0 62.003 54.621 A3.062 3.062 0 0 0 59.161 56.689 A73.49 73.49 0 0 0 56.170 92.578 A2.654 2.654 0 0 1 51.111 94.052 A36.74 36.74 0 0 1 52.093 63.128 A1.225 1.225 0 0 0 52.182 62.260 L48.938 50.153 A1.429 1.429 0 0 0 47.187 49.142 L35.080 52.387 A1.225 1.225 0 0 0 34.373 52.898 A36.74 36.74 0 0 1 8.083 69.210 A2.654 2.654 0 0 1 6.830 64.091 A73.49 73.49 0 0 0 36.416 43.557 A3.062 3.062 0 0 0 36.785 40.062 A44.91 44.91 0 0 0 16.087 20.937 A2.654 2.654 0 0 1 16.536 15.948 A36.74 36.74 0 0 1 50.954 25.058 A2.552 2.552 0 0 0 54.969 24.423 A6.634 6.634 0 0 1 64.133 21.813 Z" fill="#ffffff"/></svg>
  Sign in with Dazr Identity
</a>
Dazr font. The button uses the Dazr font, which is free to use under the SIL Open Font License. Where Dazr is not loaded, the system font is used instead. Download the Dazr font (ZIP with TTF and WOFF2 files) to host it on your own site:
/* woff2 files from the ZIP, copied to /fonts/ on your site */
@font-face { font-family: 'Dazr'; font-weight: 400; font-display: swap;
  src: url('/fonts/dazr-regular-latin.woff2') format('woff2'); }
@font-face { font-family: 'Dazr'; font-weight: 700; font-display: swap;
  src: url('/fonts/dazr-bold-latin.woff2') format('woff2'); }
.dazr-signin { font: 600 15px/1 'Dazr', system-ui, sans-serif; }
A minimal Node.js example
Node 18 or later, no dependencies. A web server app with a client secret; for a public client, drop the Authorization header and send client_id in the body.
import crypto from 'node:crypto';
const issuer = 'https://identity.dazr.eu';
const clientId = process.env.DAZR_CLIENT_ID;
const clientSecret = process.env.DAZR_CLIENT_SECRET;
const redirectUri = 'https://app.example.eu/auth/dazr/callback';
const b64url = (buf) => Buffer.from(buf).toString('base64url');

// 1. Start: keep verifier, state and nonce in the user's session.
export function start(session) {
  session.verifier = b64url(crypto.randomBytes(32));
  session.state = b64url(crypto.randomBytes(16));
  session.nonce = b64url(crypto.randomBytes(16));
  const challenge = b64url(crypto.createHash('sha256').update(session.verifier).digest());
  return issuer + '/oauth/authorize?' + new URLSearchParams({
    response_type: 'code', client_id: clientId, redirect_uri: redirectUri,
    scope: 'openid profile email', state: session.state, nonce: session.nonce,
    code_challenge: challenge, code_challenge_method: 'S256',
  });
}

// 2. Callback: check state, exchange the code, verify the ID token.
export async function callback(session, query) {
  if (query.error) throw new Error('sign-in failed: ' + query.error);
  if (query.state !== session.state || query.iss !== issuer) throw new Error('state or issuer mismatch');
  const res = await fetch(issuer + '/oauth/token', {
    method: 'POST',
    headers: {
      'Content-Type': 'application/x-www-form-urlencoded',
      Authorization: 'Basic ' + Buffer.from(clientId + ':' + clientSecret).toString('base64'),
    },
    body: new URLSearchParams({ grant_type: 'authorization_code', code: query.code, redirect_uri: redirectUri, code_verifier: session.verifier }),
  });
  const tokens = await res.json();
  if (!res.ok) throw new Error(tokens.error);
  const claims = await verifyIdToken(tokens.id_token, session.nonce);
  return { sub: claims.sub, email: claims.email, name: claims.name, tokens };
}

async function verifyIdToken(idToken, nonce) {
  const [h, p, s] = idToken.split('.');
  const header = JSON.parse(Buffer.from(h, 'base64url'));
  const { keys } = await (await fetch(issuer + '/oauth/jwks')).json();
  const jwk = keys.find((k) => k.kid === header.kid);
  if (!jwk || header.alg !== 'ES256') throw new Error('unknown signing key');
  const ok = crypto.verify('sha256', Buffer.from(h + '.' + p),
    { key: crypto.createPublicKey({ key: jwk, format: 'jwk' }), dsaEncoding: 'ieee-p1363' }, Buffer.from(s, 'base64url'));
  const c = JSON.parse(Buffer.from(p, 'base64url'));
  const now = Math.floor(Date.now() / 1000);
  if (!ok || c.iss !== issuer || c.aud !== clientId || c.exp < now - 30 || c.nonce !== nonce) throw new Error('invalid ID token');
  return c;
}
Limits
The authorization and token endpoints are rate limited. If you get HTTP 429, wait and try again; do not retry in a tight loop.
| Endpoint | Limit |
|---|---|
/oauth/authorize | 120 requests a minute per IP address |
/oauth/token | 600 requests a minute per IP address, and 300 a minute per app |
/oauth/userinfo | 1,200 requests a minute per IP address |
/oauth/verification-report | 120 requests a minute per IP address, and 60 an hour per app |
| Business verification | 6 starts an hour per person, and 10 a day per organisation |
| Test webhooks | 30 every 10 minutes per person |
Your obligations
Your organisation is an independent controller for the data it receives. The Dazr Identity Developer Terms set out what you may do with it, how to keep it secure and how to report breaches. Questions: hello@dazr.eu.
For your security and legal review: the security and procurement pack.